IAM vs IGA vs PAM: Key Differences, Use Cases, and How They Work Together
IAM, IGA, and PAM play different roles in identity security. Explore their key differences, core capabilities, enterprise use cases, popular tools, and how they work together to manage access, govern permissions, and protect privileged accounts.
CISSP vs CISM: Which Certification Fits Your Cybersecurity Career?
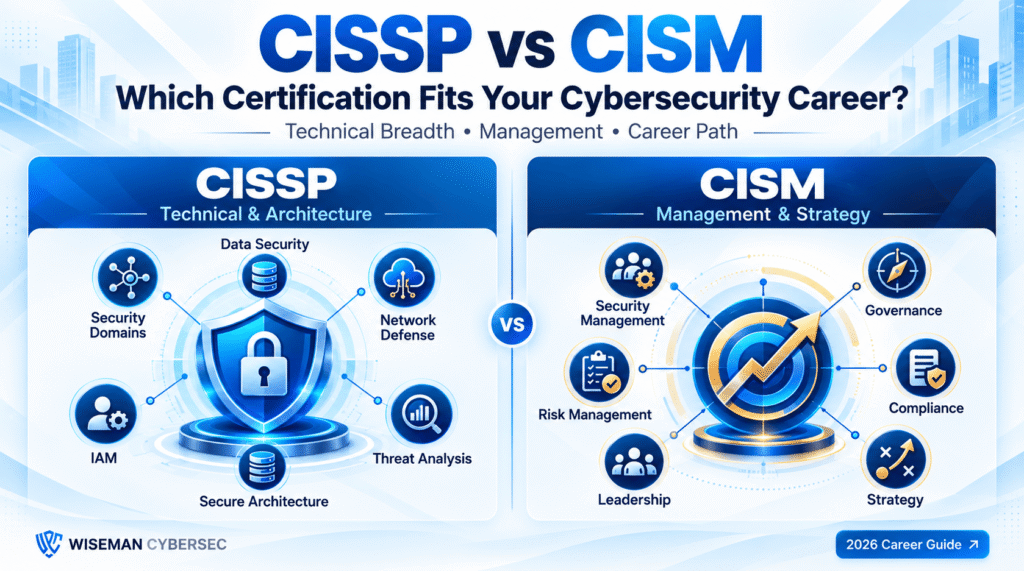
CISSP and CISM are leading cybersecurity certifications with different career focuses. Compare their domains, eligibility, difficulty, career paths, and benefits to choose the right certification for your goals.
SAML vs OAuth vs OIDC: The One-Minute Difference
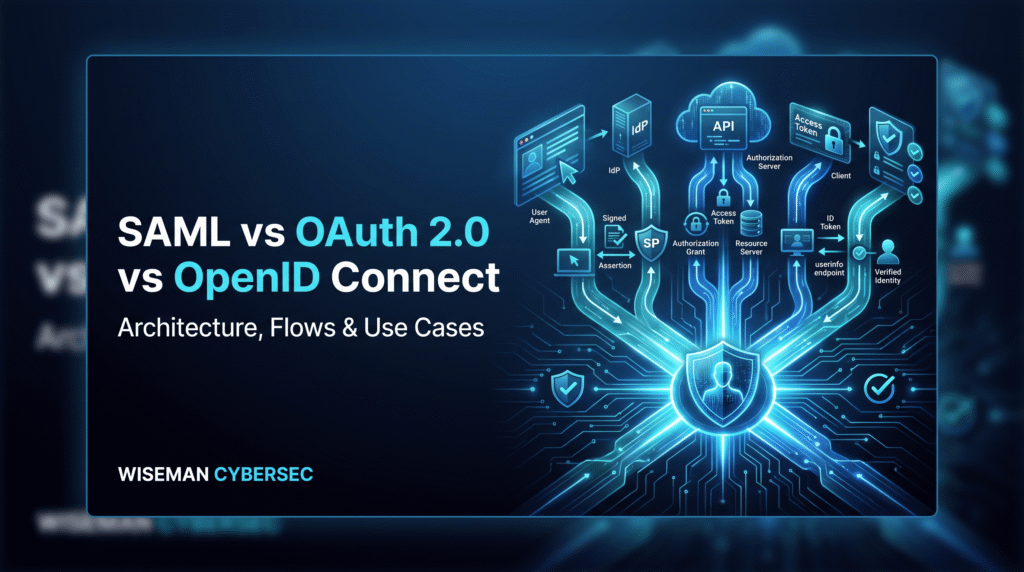
Understand the differences between SAML, OAuth 2.0 and OpenID Connect, including their purpose, authentication and authorization flows, common use cases, security considerations, and when to use each protocol.
IAM Career Roadmap: Skills, Tools, Projects and Roles from Beginner to Architect
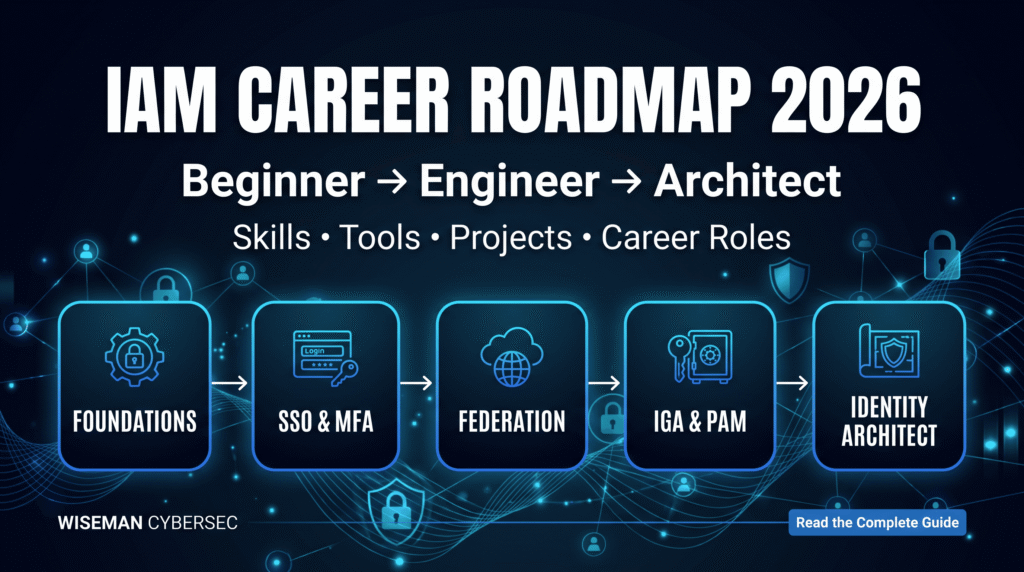
Discover a practical IAM career roadmap covering the skills, tools, projects, certifications and job roles needed to progress from IAM beginner to identity security architect. Learn authentication, authorization, SSO, MFA, federation, provisioning, IGA, PAM, cloud identity and more through a structured 90-day learning plan.
The Helpdesk Is Calling — But It’s the Attacker
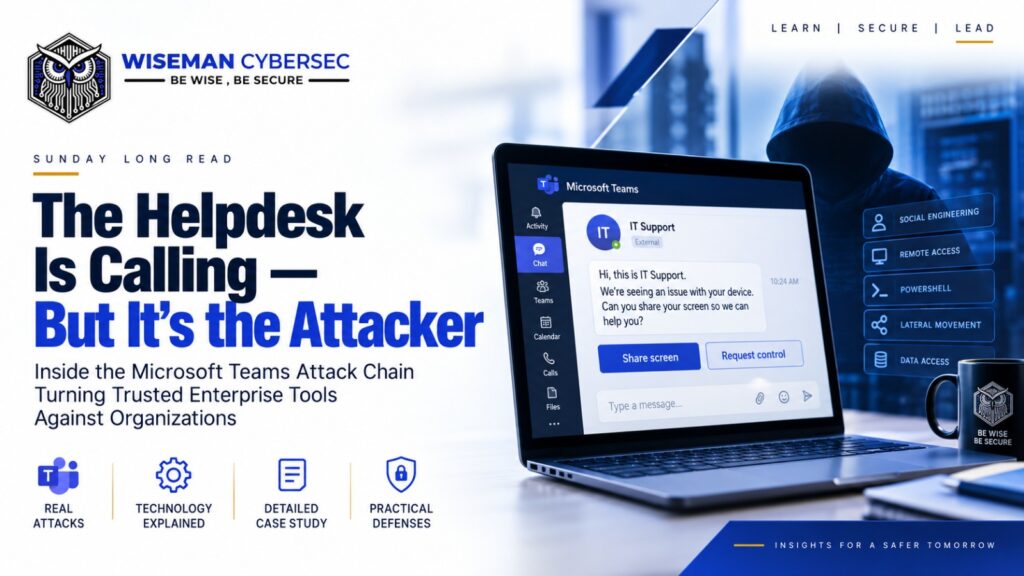
Attackers are increasingly exploiting trusted enterprise tools instead of relying on traditional malware. Explore how a Microsoft Teams helpdesk impersonation campaign can lead from remote access to Active Directory reconnaissance and lateral movement across an organization.
Identity Security as a Career:From Active Directory to Cloud IAM, PAM & Architecture
Learn how organisations can prepare for India’s DPDP framework through data mapping, consent management, retention, vendor governance, cybersecurity, and privacy ownership.
DPDP Compliance Is Moving From Policy to Practice:Is Your Organisation Actually Ready?
Learn how organisations can prepare for India’s DPDP framework through data mapping, consent management, retention, vendor governance, cybersecurity, and privacy ownership.
Third-Party Risk Management (TPRM) –
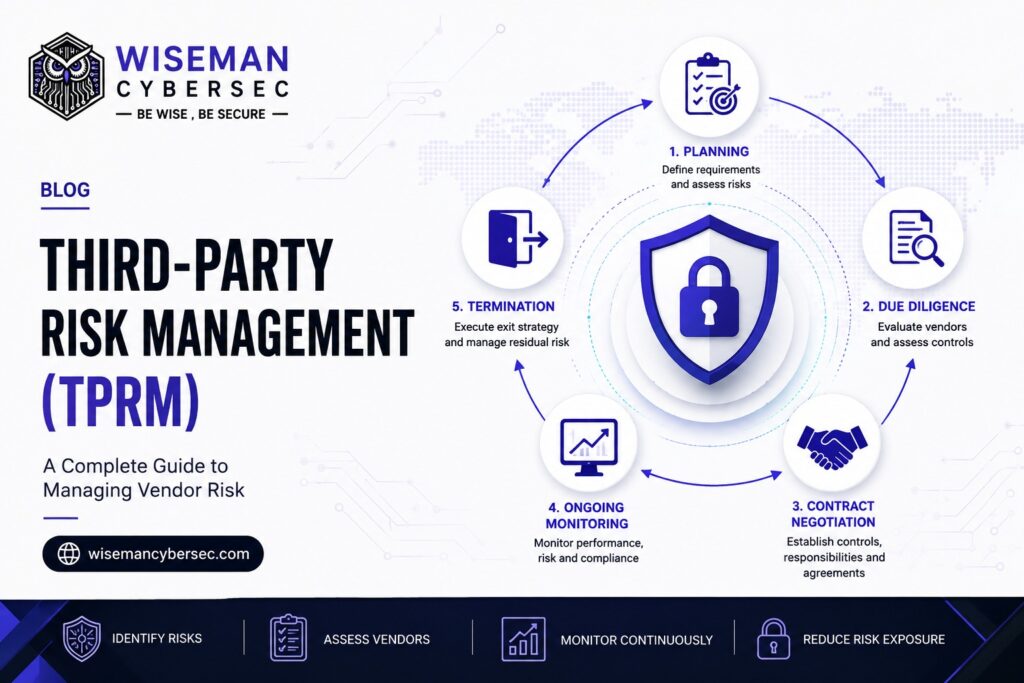
Learn how to identify, assess, monitor, and manage third-party risks across the entire vendor lifecycle—from due diligence and contract negotiation to ongoing monitoring and secure termination.
Vibe Coding Is Creating a Shadow Application-Security Crisis
Vibe coding is accelerating software development, but faster coding can introduce serious security risks. Discover how AI-generated code can create hidden application security vulnerabilities and why security must keep pace with development.
Your AI Agent Has Access—But Should It?
Agentic AI is transforming cybersecurity by giving AI systems the ability to access data, use tools, and take autonomous actions. Explore the seven critical security risks of agentic AI and the practical controls organisations can use to secure AI agents.