DFIR Training – Digital Forensics & Incident Response
Build practical DFIR skills in digital forensics, incident response, evidence analysis, and real-world cyber investigations.
Expert Trainers
Industry Experienced
Hands-on Labs
Real-world Practice
Certification Support
Exam Aligned Content
Lifetime Support
Post Training Assistance
UPCOMING BATCH (Weekend Only)
Batch date
Batch Timing (IST)
Duration
Mode
7th November
7:00 PM – 10:00 PM
48 Hours
Live Online
31st October
7:00 PM – 10:00 PM
12 Hours
Live Online
Course Overview
Our DFIR training program provides a practical journey into digital forensics and incident response, covering digital evidence, forensic investigation, incident handling, and advanced investigation techniques. Through interactive sessions and hands-on labs, you’ll learn to investigate cyber incidents, preserve evidence, analyze systems, and respond effectively to security breaches.
✓ Digital Forensics & Incident Response Fundamentals
✓ Hands-On Investigation & Forensic Labs
✓ Disk, Memory & Network Forensics
✓ Cloud, Database & Mobile Forensics
✓ Evidence Collection, Analysis & Reporting
✓ Advanced DFIR Tools & Investigation Techniques
✓ Real-World Incident Response & Case-Based Learning
Key Highlights
52+ Hours of Live Training
Real‑World Forensics Labs
High Success Rate & Certification Support
Expert DFIR Industry Instructors
Comprehensive Curriculum & Materials
Practical Case Studies & Simulations
Certification & Exam Support
Mentorship & Community
Post‑Course Career Support
Skills You’ll Learn
Evidence Collection & Preservation
Learn evidence handling, chain of custody, acquisition methods, validation, and forensic integrity.
Disk & File System Forensics
Analyze disk structures, file systems, deleted data, file carving, RAID, NAS, and data recovery.
Memory & Malware Forensics
Acquire and analyze memory dumps, investigate malware activity, and uncover hidden forensic artifacts.
Network & Dark Web Forensics
Investigate network traffic, logs, indicators of compromise, TOR artifacts, and dark web activity.
Mobile & Digital Device Forensics
Perform Android and iOS forensic acquisition and investigate data from mobile and digital devices.
Advanced DFIR Tools & Techniques
Work with industry tools such as Magnet AXIOM, Cellebrite, Volatility, OSForensics, Oxygen Detective, and Amped FIVE.
Why Choose WisemanCyberSec
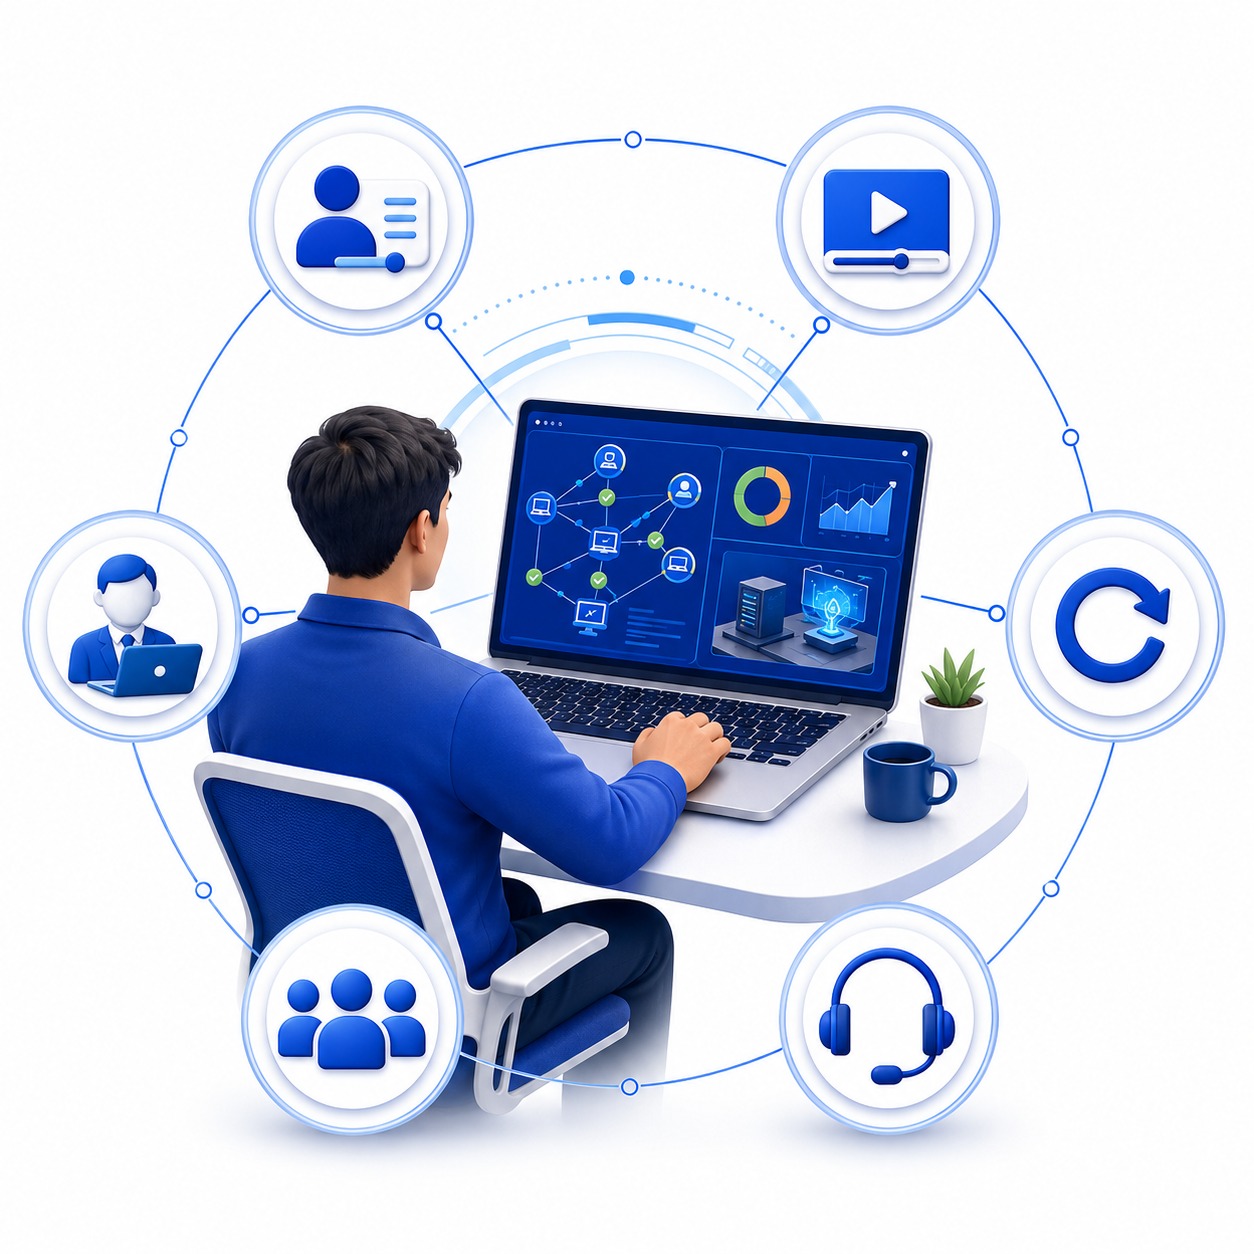
Start Your Cybersecurity Career with Confidence
Personalized Learning Experience
We keep our batch sizes limited to just 5–7 students to ensure highly interactive sessions, personalized mentorship, and proper one-to-one attention for every learner.
Flexible Redo & Retake Option
Missed a session due to work or personal commitments? No worries. Students can redo missed sessions with upcoming batches and continue learning without interruption.
LMS Access with Recorded Sessions
Get access to our dedicated LMS platform with recorded sessions, helping you revise concepts anytime and learn at your own pace whenever needed.
Continuous Post-Training Support
Our support continues even after training completion through dedicated community groups, regular communication, study resources, and continuous mentor guidance.
Join an Active Cybersecurity Community
Become part of a growing cybersecurity community with access to weekly discussions, masterclasses, expert sessions, podcasts, and networking opportunities beyond your domain.
Learn from Real Industry Experts
All our instructors have strong real-world industry experience and hands-on practical exposure, helping students learn actual tools, workflows, and business use cases.
What Our DFIR Learners Say
Discover how our DFIR training empowers cybersecurity professionals with hands-on forensic investigation skills, incident response expertise, and the confidence to tackle real-world cyber threats.
Course Curriculum
Learn the fundamentals of digital forensics, types of digital evidence, analysis steps and how to reconstruct a digital crime scene. Understand the challenges of handling digital evidence and major forensic concepts.
Study storage formats, acquisition methods (disk imaging, live acquisition), the use of write blockers, validation of evidence, exploring evidence and understanding timestamps.
Understand how attackers hide or destroy evidence. Learn about anti‑forensics techniques, data deletion, hidden data and how to counteract these measures.
Master logical and raw data recovery, recovering files from recycle bins and using carving techniques to extract data from unallocated space.
Explore disk drive types, logical structure of disks, boot processes for Windows, Linux & macOS, file system analysis using Autopsy and storage systems like RAID & NAS.
Learn NTFS, FAT, Ext, ExFAT, HFS and APFS file systems and how to analyse them.
Collect evidence from Windows systems: registry analysis, browser artefacts (cache, cookies, history), file signatures and log analysis.
Understand volatile and non‑volatile data on Linux systems, file system structures and memory acquisition.
Acquire system memory, use tools like Volatility and MemProcFS, analyse Windows and Linux memory and detect malware in memory dumps.
Discover the dark web, identify traces of TOR browser usage and perform TOR browser forensics.
Learn the importance of Android device forensics, steps to perform logical and physical data acquisition, rooting methods, analysis using Autopsy and common challenges.
Understand iOS forensic processes, including logical & physical acquisition, jailbreaking, analysis using Autopsy and challenges in iOS investigations.
- Cloud Forensics:
Investigate cloud environments (IaaS, PaaS, SaaS). - Database Forensics:
Analyse database breaches and tampering. - Linux‑Based Forensic OS:
Use specialised Linux distributions for forensics. - Professional Data Recovery:
Learn advanced data recovery techniques. - CCTV & Video Evidence Forensics:
Perform DVR extraction, convert proprietary formats, enhance video evidence and carve data from DVR disks. - Final Exam & Practical Challenge:
Apply your knowledge in a real‑world DFIR scenario to earn your certification.
Who Should Enroll
Aspiring DFIR professionals building forensic and incident response skills.
SOC and security analysts strengthening investigation skills.
Law enforcement professionals handling digital evidence.
IT and network professionals learning forensic investigation.
Cybersecurity professionals expanding into DFIR.
Students and career switchers entering cybersecurity.
Prerequisites
Comfortable with basic IT, Windows/Linux, and networking
Familiarity with fundamental cybersecurity concepts
Basic Python or scripting knowledge is helpful
Strong interest in cybersecurity and digital investigations
GET A FREE DEMO CLASS
Training Format & Delivery
The DFIR training is available through personalized one-on-one sessions, with flexible scheduling to suit individual learning needs. Sessions combine expert guidance, practical labs, and real-world investigation scenarios.
What to Expect
Explore digital evidence collection, disk and memory forensics, network investigations, mobile forensics, and incident response. Learn to investigate cyber incidents through hands-on labs and practical case studies. wisemancybersec.com
Practical & Career-Focused Learning
Build job-ready skills for roles such as Digital Forensic Analyst, Incident Responder, SOC Analyst, and Security Consultant. Gain practical knowledge to strengthen your cybersecurity expertise and career opportunities.
Hands‑On Experience
Work with forensic tools and techniques for data acquisition, evidence preservation, memory analysis, and malware investigations. Practice real-world scenarios to develop confidence in digital investigations and incident handling.
DFIR Career Path & Growth Cycle
Digital Forensics & Incident Response (DFIR) offers diverse career paths across forensic investigation, incident response, threat analysis, and cybersecurity leadership. Professionals can progress from analyzing digital evidence to leading complex investigations and enterprise incident response programs.
DFIR Analyst
(Entry Level)
Incident Responder
(Mid Level)
Digital Forensics Investigator
(Senior Level)
DFIR Specialist
(Leadership)
DFIR Lead / Security Consultant
(PAM, Cloud)
Frequently Asked Questions
DFIR is the practice of investigating cyber incidents, collecting digital evidence and responding to breaches. Certifications like CHFI and GCFA are internationally recognized credentials.
No prior work experience is required to join the DFIR course; we welcome beginners and experienced professionals alike. For the exam, completing our official training satisfies eligibility requirements.
Most DFIR batches are delivered as live online instructor‑led classes. In‑person classroom bootcamps and 1‑ 1 training options are available upon request. All formats include remote lab access for hands‑on practice.
Absolutely! Hands‑on labs are central to our DFIR program. You will practice data acquisition, memory analysis, disk forensics, mobile forensics and network investigations in safe virtual labs.
You will have lifetime access to e-courseware and class recordings. Lab access is provided for several months after training with options to extend or set up a home lab.
Common roles include Digital Forensic Analyst, Incident Responder, SOC Analyst, Malware Analyst and Security Consultant. Some roles may require additional experience, but the DFIR certification significantly strengthens your profile.
Become a Digital Forensics & Incident Response Professional
Master practical DFIR skills through hands-on labs, real-world investigations, and advanced forensic tools with guidance from experienced professionals.
WisemanCyberSec is a dedicated platform for cybersecurity education and awareness, empowering individuals and organizations to stay secure in the digital world.