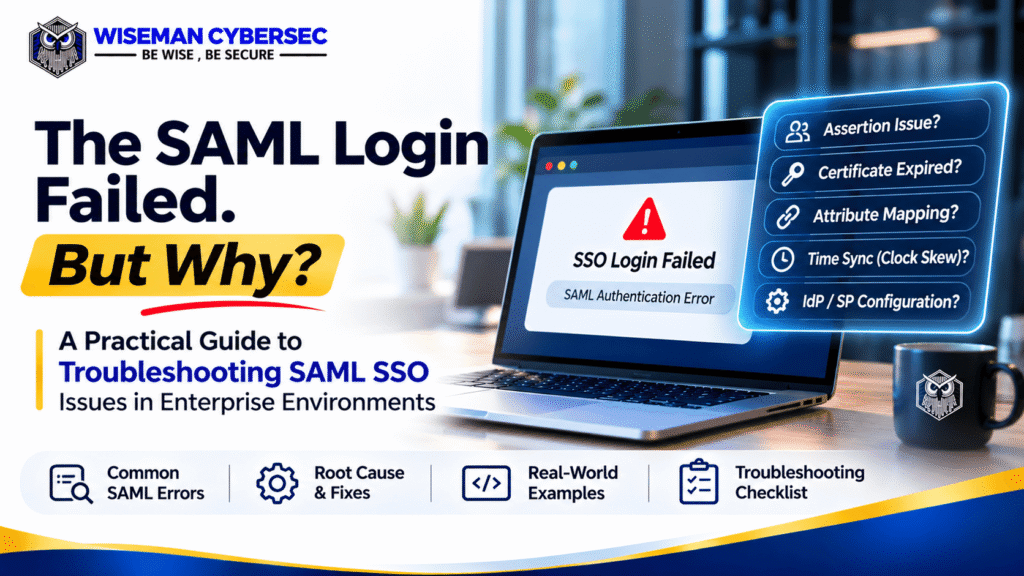
Your SAML Single Sign-On (SSO) worked yesterday. Today, users can’t log in. What went wrong?
SAML authentication failures are common challenges for IAM engineers working with Microsoft Entra ID, Okta, and enterprise applications.
A successful password authentication doesn’t always mean SSO will work. Problems with certificates, metadata, attributes, or application configuration can prevent a service provider from accepting a SAML response.
In this guide, we’ll explore 7 common SAML SSO errors, their causes, and practical troubleshooting steps.
1. SAML Certificate Expired or Incorrect
Scenario: Users successfully authenticate with their identity provider (IdP), but the application rejects the SAML response.
Possible cause: The service provider (SP) no longer trusts the signing certificate used by the IdP.
How to troubleshoot:
- Check the IdP’s active SAML signing certificate.
- Verify that the SP trusts the corresponding certificate.
- Review recent certificate rotations and metadata updates.
- Confirm that the signature validates.
Practical tip: A certificate rotation can interrupt SSO if the IdP and SP configurations are not synchronized.
2. Incorrect Assertion Consumer Service (ACS) URL
Scenario: Users authenticate successfully but are redirected to an error page.
Possible cause: The configured ACS URL doesn’t match the endpoint the application expects.
The ACS URL is where the SP receives the SAML response.
How to troubleshoot:
- Compare the ACS URL configured in the IdP with the SP configuration.
- Check the Destination and Recipient values where applicable.
- Look for incorrect paths, domains, or environment-specific URLs.
Practical tip: Even a small URL mismatch can cause authentication failure.
3. Audience or Entity ID Mismatch
Scenario: The application receives a SAML assertion but rejects it as invalid.
Possible cause: The assertion’s intended audience doesn’t match the SP’s configured Entity ID.
How to troubleshoot:
- Identify the SP Entity ID.
- Inspect the assertion’s AudienceRestriction value.
- Check whether production and test configurations have been mixed.
Practical tip: The audience must match the identity of the intended service provider.
4. Incorrect NameID or Attribute Mapping
Scenario: SAML authentication appears successful, but the application cannot identify the user.
Possible cause: The application expects a different NameID format or required attribute.
For example, the IdP sends:
employee123
But the application expects:
employee123@example.com
How to troubleshoot:
- Inspect the NameID format and value.
- Verify required attributes such as email, username, or groups.
- Compare the assertion with the application’s documented requirements.
Practical tip: Authentication can succeed at the IdP while user identification fails at the application.
5. SAML Assertion Time Validation Failure
Scenario: Users encounter an expired assertion or assertion-not-yet-valid error.
Possible cause: The assertion falls outside the SP’s permitted validity window, potentially because of clock synchronization issues.
How to troubleshoot:
- Review NotBefore and NotOnOrAfter conditions.
- Verify server clock synchronization.
- Check the SP’s supported clock-skew tolerance.
Practical tip: Ensure systems use reliable time synchronization. Avoid weakening assertion validation to bypass the error.
6. User Not Assigned or Provisioned to the Application
Scenario: One employee cannot access the application, while colleagues can.
Possible cause: The user lacks an appropriate application assignment, required account, or permission.
How to troubleshoot:
- Check the user’s application assignment in Entra ID or Okta.
- Confirm that the account exists in the target application.
- Review provisioning status and relevant role or group mappings.
Practical tip: A successful SAML response doesn’t necessarily guarantee authorization within the target application.
7. Incorrect IdP/SP Configuration or Metadata
Scenario: SSO stops working after an application migration or configuration change.
Possible cause: The IdP and SP configurations no longer agree on identifiers, certificates, endpoints, or required bindings.
How to troubleshoot:
- Compare current IdP and SP metadata.
- Review recent configuration changes.
- Verify signing settings and supported SAML bindings.
- Test the configured SSO flow after applying approved corrections.
Practical tip: Treat SAML metadata changes as controlled production changes, especially when several applications depend on the same identity provider.
Real-World Example: SAML Login Worked Yesterday
Consider this illustrative enterprise scenario.
An organization uses Microsoft Entra ID for SSO to a business application.
Employees suddenly report authentication errors.
The IAM engineer investigates and discovers:
- Users authenticate successfully with Entra ID.
- The application receives a SAML response.
- The application’s trusted signing certificate configuration is outdated.
- Entra ID has started signing responses using a replacement certificate.
Root cause: The SP doesn’t trust the certificate currently used to sign the SAML response.
Resolution: The administrator updates the SP’s trusted signing certificate through the approved certificate-rollover procedure and verifies the SSO flow.
Key lesson: Always investigate the complete authentication flow before assuming the problem is a user’s password or account.
Quick SAML SSO Troubleshooting Checklist
When SAML authentication fails, follow this sequence:
- Identify where the failure occurs: At the IdP, during response processing, or inside the application?
- Review authentication logs: Check Entra ID sign-in logs or Okta System Log.
- Inspect the SAML exchange: Use an approved SAML tracing tool to examine the request and response.
- Validate critical fields: ACS URL, Entity ID, Audience, NameID, Destination, and signing certificate.
- Verify the user: Check assignments, provisioning, and application permissions.
- Confirm the fix: Repeat the login test and review the resulting logs.
Security note: SAML assertions may contain sensitive identity information and can sometimes function as authentication credentials. Never upload production assertions to untrusted public tools. Use authorized tracing methods and sanitize diagnostic evidence.
Frequently Asked Questions
Ques: What causes SAML authentication to fail?
Common causes include incorrect SAML configuration, signing certificate issues, ACS URL mismatches, invalid assertions, and missing user attributes.
Ques: How do I troubleshoot SAML SSO in Microsoft Entra ID?
Start with the application’s configuration and Entra sign-in logs. Then inspect the SAML response, validate certificates and URLs, and check the user’s assignment.
Ques: Can SAML authentication succeed while application access fails?
Yes. The IdP may authenticate the user successfully, while the SP rejects the assertion or denies application access because of missing user mapping, provisioning, or permissions.
Final Thoughts
SAML SSO troubleshooting is not about randomly changing configurations until the login works.
It’s about identifying the exact point of failure, understanding the authentication flow, and validating the root cause. For IAM professionals, these troubleshooting skills are essential when working with enterprise identity platforms.