Prepare for SOC Analyst L1 interviews with 20 practical questions covering SIEM, logs, alert triage, EDR, phishing, escalation and incident response.
Quick Insights Interviewers are testing structured investigation thinking, not only memorized definitions. A strong L1 answer explains what to validate, how to scope the activity, when to escalate and what to document. Core preparation areas include SIEM searches, identity and endpoint evidence, network logs, phishing, threat intelligence and incident-response communication. Knowing the boundary of L1 authority is a strength. Safe escalation is better than unsupported containment. What Interviewers Really Look For SOC interviews are moving beyond definitions. Employers want analysts who can turn an alert into a defensible investigation: validate the telemetry, correlate evidence, manage uncertainty, communicate clearly and escalate at the right time. An L1 or Tier 1 SOC Analyst is usually the first human checkpoint in the detection-and-response workflow. The role requires networking and operating-system fundamentals, but technical knowledge alone is not enough. Analysts must distinguish unusual activity from malicious activity, preserve evidence, work within authorization boundaries and leave behind a ticket that another analyst can trust. The questions below are designed as model answers, not scripts to memorize. Adapt them to the tools, playbooks and responsibilities of the organization interviewing you. A Simple Framework for Scenario Questions Use V-SCOPE: Validate the alert; Scope users, assets and time; Correlate evidence; Observe behavior and context; Prioritize and preserve; Escalate with clear documentation. This framework prevents two common interview mistakes: jumping directly to a conclusion and proposing a disruptive action before understanding scope, authority or business impact. 20 SOC Analyst L1 Interview Questions and Answers What is the role of an L1 SOC Analyst? An L1 SOC Analyst is usually the first operational reviewer of security alerts. The analyst monitors the alert queue, validates whether the detection has enough evidence, gathers context about the user, device, IP address and affected service, records a clear disposition, and escalates cases that exceed L1 authority or require deeper investigation. A strong answer should also mention boundaries. L1 analysts follow playbooks and escalation procedures; they should not perform disruptive containment actions simply because an alert looks suspicious. Their value comes from accurate triage, evidence preservation, timely escalation, clean documentation and reliable shift handover. What is the difference between an event, an alert and an incident? An event is an observable occurrence, such as a login, process creation, DNS query or firewall connection. An alert is generated when a detection rule, analytic or security product identifies activity that may require investigation. An incident is a confirmed or reasonably suspected cybersecurity occurrence that requires coordinated response under the organization’s criteria. Not every event becomes an alert, and not every alert becomes an incident. The analyst’s job is to evaluate evidence and context before assigning a disposition. Treating every alert as an incident creates noise; dismissing alerts without validation creates risk. What is a SIEM, and how does an L1 analyst use it? A Security Information and Event Management platform collects and centralizes security-relevant data, normalizes or parses fields, supports search and correlation, and generates alerts or cases. An L1 analyst uses the SIEM to review detection logic, search related activity, build a timeline and connect evidence across identity, endpoint, network, email, cloud and application sources. A SIEM does not replace analyst judgment. The quality of an investigation depends on log coverage, timestamp consistency, parsing accuracy, asset context and detection design. A polished interview answer should explain both what the platform enables and where its limitations begin. What fields do you check first when opening an alert? Start with the alert time and timezone, detection name, rule logic, affected user and host, source and destination IP addresses, ports, process or command line, action or result, severity, confidence and asset criticality. Then look for related alerts, recent changes, previous activity and the normal baseline for the entity. The exact fields vary by use case. A failed-login alert requires authentication status, logon type and source context; an endpoint alert requires process-tree and file information. The key is to avoid investigating one isolated field without establishing who, what, where, when and expected behavior. Walk me through your alert-triage process. First, validate that the alert and underlying telemetry are complete. Next, scope the affected users, hosts, IP addresses and time window. Correlate activity across relevant sources, enrich important observables, compare the behavior with known baselines and approved changes, and build a short timeline. Then classify the alert as a true positive, benign positive, false positive or inconclusive case; assign severity and priority using business context; recommend or take only authorized actions; and document the evidence, reasoning, limitations and next step. Escalation should contain enough information for the receiving analyst to continue without repeating the entire investigation. What is the difference between a true positive, false positive and benign positive? A true positive means the detection correctly identified activity that is malicious or violates security policy. A false positive means the detection incorrectly flagged activity because the rule logic, threshold, data quality or context was wrong. A benign positive means the detection correctly identified the behavior, but the activity was expected and authorized, such as a sanctioned administrative script. This distinction matters for detection improvement. A false positive may require logic or parsing changes; a benign positive may require approved contextual suppression while preserving coverage for unauthorized use. The analyst should document the evidence supporting the disposition rather than selecting a closure reason by habit. How are alert severity and investigation priority different? Severity represents the potential or observed impact of the activity. Priority determines the order in which the SOC should work the case. Priority considers severity together with confidence, asset criticality, user privilege, scope, business impact, regulatory sensitivity and time pressure. For example, a technically moderate alert affecting a domain administrator or critical production server may receive a higher priority than a high-volume alert on a low-value test system. A mature analyst does not rely on the vendor’s default severity alone; they apply organizational context. How would you tune a noisy detection without disabling it? Measure the alert volume and review a representative sample to identify why the rule
Harvest Now, Decrypt Later: Why Post-Quantum Migration Cannot Wait Until Quantum Computers Arrive
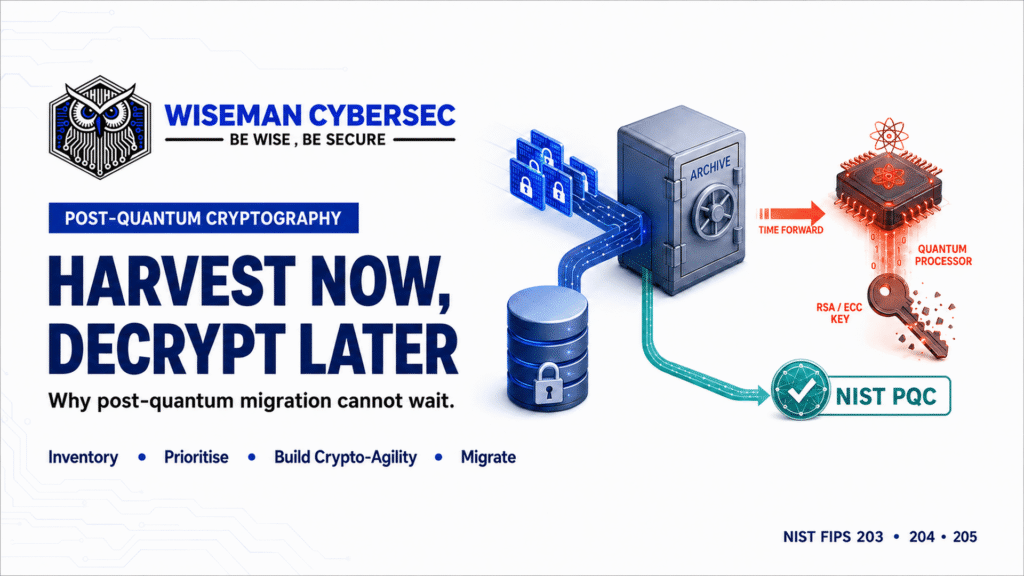
Some cybersecurity risks become urgent only after the technology behind them becomes available. Post-quantum risk is different. Sensitive information can be stolen today, stored for years and decrypted later when sufficiently capable quantum computers become available. By that point, changing the encryption algorithm will protect future data—but it will not restore the confidentiality of information already collected. This threat is known as Harvest Now, Decrypt Later, or HNDL. For organisations handling long-life health records, identity data, financial information, government communications, intellectual property or strategic business information, the post-quantum deadline may have already started. What Is “Harvest Now, Decrypt Later”? In an HNDL attack, an adversary does not need to break encryption immediately. The attacker may: Today, strong cryptography may prevent the attacker from reading that information. However, the attacker can preserve the ciphertext until more powerful computing capabilities become available. A cryptographically relevant quantum computer could eventually threaten widely used public-key algorithms based on integer factorisation and discrete logarithms. These include RSA, Diffie-Hellman, elliptic-curve Diffie-Hellman and elliptic-curve digital signatures. NIST specifically identifies sensitive or long-lived data protected by quantum-vulnerable cryptography as being exposed to the The attack therefore begins when the encrypted information is collected—not when quantum decryption finally becomes possible. Why Long-Life Data Creates an Immediate Risk Not every piece of information has the same confidentiality period. A promotional email may lose its value within weeks. A customer password can be changed. But other information may remain sensitive for ten, twenty or even thirty years. Examples include: If this information is stolen today and must remain confidential beyond the useful life of its current encryption, the organisation already has a post-quantum exposure. This is why quantum readiness cannot be based only on predicting when a powerful quantum computer will arrive. That date remains uncertain. The more important question is: How long must the data remain confidential, and how long will the organisation need to complete its migration? If the combined data-protection period and migration time extend into the possible quantum-risk window, waiting is not a safe strategy. Quantum Risk Is Not Limited to Decryption Post-quantum discussions often focus only on encrypted data. However, public-key cryptography also protects digital trust. Digital signatures are used to verify software updates, certificates, transactions, documents, devices, users and code. If quantum-vulnerable signature algorithms are compromised, attackers may be able to forge trusted identities or malicious content. Potential consequences include: Post-quantum migration must therefore address both sides of public-key cryptography: Simply replacing an encryption library in one application will not solve the wider problem. NIST’s Post-Quantum Cryptography Standards In August 2024, NIST published its first three principal post-quantum cryptography standards. NIST now states that these algorithms can and should be put into use as organisations begin their migration. ML-KEM — FIPS 203 ML-KEM is a module-lattice-based key-encapsulation mechanism. It allows two parties to establish a shared secret over a public channel. That shared secret can then be used with symmetric cryptography to protect communications. ML-KEM is intended to address quantum risk in key-establishment scenarios such as secure communication protocols, VPNs and other encrypted connections. ML-DSA — FIPS 204 ML-DSA is a module-lattice-based digital-signature algorithm. It is designed to protect the authenticity and integrity of digital information and is expected to support many post-quantum signature deployments. SLH-DSA — FIPS 205 SLH-DSA is a stateless hash-based digital-signature algorithm. Because it is based on a different mathematical approach, it provides an alternative to ML-DSA for appropriate use cases and contributes to cryptographic diversity. These standards provide a foundation, but publishing an algorithm is not the same as completing an enterprise migration. Products, protocols, applications, certificates, hardware and vendor services must all be updated and tested. Migration Begins With a Cryptographic Inventory An organisation cannot migrate cryptography it cannot locate. Cryptographic functions may exist across applications, APIs, cloud services, certificates, VPNs, databases, identity systems, hardware security modules, embedded devices, source code and third-party platforms. Some implementations are visible and centrally managed. Others may be buried inside legacy applications, vendor products or undocumented dependencies. A useful cryptographic inventory should identify: NIST’s National Cybersecurity Center of Excellence is specifically working on cryptographic discovery tools and inventories to help organisations locate quantum-vulnerable cryptography and prioritise migration decisions. The inventory should not be treated as a one-time spreadsheet. It must become part of continuing security architecture, asset management and procurement processes. Prioritise According to Risk, Not Convenience Attempting to replace every cryptographic implementation simultaneously would create unnecessary operational risk. Migration should be prioritised according to: Systems protecting long-life sensitive information should receive early attention. Organisations should also prioritise long-lived infrastructure such as public-key infrastructure, code-signing systems, identity platforms, VPNs, TLS environments, hardware devices and operational technology. These systems may remain deployed for many years and can be difficult to replace quickly. Crypto-Agility Must Become an Architectural Requirement Post-quantum migration should not result in another generation of systems permanently tied to a single algorithm. Algorithms may be weakened, standards may evolve and implementation defects may be discovered. Organisations must be able to change cryptographic components without rebuilding entire systems or causing lengthy service interruptions. NIST defines crypto-agility as the capability to replace and adapt cryptographic algorithms across protocols, applications, software, hardware, firmware and infrastructure while preserving security and ongoing operations. Its guidance was most recently updated in June 2026. Practical crypto-agility may include: Crypto-agility is not merely a post-quantum control. It strengthens the organisation’s ability to respond to any future cryptographic vulnerability or transition. A Practical Post-Quantum Migration Roadmap Organisations do not need to replace every algorithm immediately. They do need a structured programme. 1. Establish ownership Assign responsibility for post-quantum readiness across security, architecture, infrastructure, application development, risk, compliance and procurement teams. 2. Build the cryptographic inventory Identify where RSA, Diffie-Hellman, ECC and other quantum-vulnerable public-key mechanisms are used across internal and third-party environments. 3. Classify data by protection lifetime Determine which information must remain confidential for years or decades. Prioritise data with long-term legal, strategic, financial or personal value. 4. Assess vendor readiness Ask technology providers which NIST-standardised algorithms they support,
AI Agents Are the New Privileged Identities: Is Your IAM Strategy Ready?
For years, organizations have focused on securing human users, service accounts, applications and machines. Now, a new category of identity is entering the enterprise: the AI agent. Unlike traditional AI assistants that mainly generate answers, agentic AI systems can reason, make decisions, access applications, retrieve sensitive data, call APIs and execute actions with limited human involvement. An AI agent may soon be able to: This capability can deliver significant productivity improvements. It can also create a new class of highly privileged, autonomous identities. The question is no longer only, “Is the AI model secure?” Organizations must also ask:Who is the agent, what is it permitted to access, who is responsible for it and how can its authority be withdrawn? From Model Risk to Action Risk Traditional generative AI security often focuses on risks such as prompt injection, sensitive-information disclosure, insecure output handling and data poisoning. Agentic AI expands the problem. An agent does not simply produce content. It can translate that content into action by using tools, credentials, APIs and enterprise applications. A manipulated chatbot may provide an incorrect response. A manipulated AI agent could change a configuration, disclose sensitive information, delete data or execute an unauthorized transaction. This is the difference between model risk and action risk. The greater an agent’s autonomy, connectivity and access privileges, the greater its potential blast radius. Recognizing this shift, NIST launched its AI Agent Standards Initiative in 2026 and began examining how established identity and authorization practices can be applied to software and AI agents. OWASP’s Top 10 for Agentic Applications also highlights risks such as agent goal hijacking, tool misuse, identity and privilege abuse, memory poisoning, insecure agent communication and rogue-agent behaviour.Agent security is quickly becoming an identity-security challenge. Why Every AI Agent Needs Its Own Identity An agent should never operate as an invisible extension of a human account or through a shared, permanently privileged credential. Every production AI agent should have a unique and verifiable identity. That identity should establish: Separate identities make it possible to enforce least privilege, monitor behaviour, investigate incidents and revoke access without affecting unrelated users or agents. If multiple agents share the same identity, security teams may be unable to determine which agent performed an action or whether it was initiated by a user, an agent or a compromised integration.Accountability begins with identity. Five Identity Risks Created by AI Agents 1. Excessive privileges Agents are often given broad access because developers want them to complete workflows without interruptions. An agent that only needs to read support tickets should not be able to delete them. An agent that recommends cloud changes should not automatically have permission to deploy those changes. Convenience must not replace least privilege. 2. Agent sprawl Business teams may create AI agents faster than security and IT teams can discover or govern them. Without a central inventory, organizations can accumulate unknown, duplicated or abandoned agents connected to sensitive systems. This resembles service-account sprawl, but with an added layer of autonomy. 3. Shared or inherited credentials An agent may inherit the permissions of its creator or use a shared API key. If the agent is compromised, an attacker may gain the same access. Long-lived credentials also make revocation and attribution more difficult. 4. Goal hijacking and tool misuse Malicious instructions hidden inside emails, documents, websites or external data can influence an agent’s behaviour. If the agent can access powerful tools, manipulated instructions may lead to unauthorized data retrieval, message sending, code execution or configuration changes. 5. Incomplete audit trails Traditional logs may record that an API was called without explaining which agent initiated it, which user request triggered the action or what information influenced the decision. Security teams need visibility across the complete chain: Human request → Agent decision → Tool invocation → System action → Business outcomeWithout this context, investigation and accountability become extremely difficult. Building an Identity-First Security Model for AI Agents Organizations do not need to abandon their existing security foundations. They need to extend them to autonomous systems. A practical identity-first approach should include the following controls. Discover and classify every agent Maintain a central inventory of production and experimental agents. Record the agent’s owner, purpose, environment, connected systems, data access, model, tools and operational risk. Assign a unique identity Every agent should have its own managed identity rather than using a shared account or impersonating its creator. The organization must be able to distinguish between: Enforce least-privilege access Access should be limited by task, resource, environment, time and risk. An agent should receive only the permissions required for its approved purpose. Privileged access should be temporary wherever possible. Introduce approval gates High-impact activities should require explicit human approval. These may include: Autonomy should be proportional to risk. Protect credentials and tokens API keys, secrets and access tokens should be stored in approved secrets-management systems, rotated regularly and prevented from appearing in prompts, memory or logs. Short-lived credentials are preferable to permanent access. Monitor agent behaviour Security teams should establish normal behaviour for each agent and detect unusual actions, access patterns, tool usage or data movement. Logs should capture the agent identity, initiating user, requested objective, tools invoked, resources accessed and final action. Govern the complete lifecycle Agents should be provisioned, reviewed and decommissioned through a controlled lifecycle. When an owner leaves, a project ends or an agent is no longer required, its credentials and access must be revoked immediately. Test before granting autonomy Organizations should evaluate agents for prompt injection, excessive agency, tool misuse, data leakage, privilege escalation and unexpected behaviour before production deployment. Security testing must cover the complete agent workflow—not only the underlying model. Questions Leaders Should Ask Today Before deploying an AI agent, security and business leaders should be able to answer: If these questions cannot be answered, the agent is not ready for unrestricted enterprise access. The Next IAM Challenge Has Already Arrived AI agents are becoming part of the enterprise workforce, but they cannot be governed exactly like employees or treated merely as
5 AI Governance Frameworks, Laws and Standards Every AIGP Candidate Should Know in 2026
Artificial intelligence adoption is accelerating faster than many organisations can establish effective governance. Bain reported in 2025 that 95% of surveyed US companies were using generative AI. The research also found that the average number of production use cases had doubled between October 2023 and December 2024. This growth creates enormous opportunities, but it also introduces risks involving privacy, cybersecurity, discrimination, transparency, accountability, intellectual property and regulatory compliance. Organisations therefore need more than an AI policy. They need structured ways to identify risks, assign accountability, evaluate impacts and monitor AI systems throughout their lifecycle. For professionals preparing for the IAPP Artificial Intelligence Governance Professional certification, understanding the major AI governance instruments is essential. However, candidates must also recognise an important distinction: A framework, regulation, standard, policy directive and code of conduct are not the same thing.This guide examines five important AI governance instruments and explains how each should be understood. 1. NIST Artificial Intelligence Risk Management Framework The NIST Artificial Intelligence Risk Management Framework, commonly called the NIST AI RMF, was released in January 2023 by the US National Institute of Standards and Technology. It is a voluntary and industry-agnostic framework designed to help organisations manage risks associated with the design, development, deployment and use of AI systems. Rather than providing a rigid compliance checklist, the framework helps organisations establish repeatable processes for trustworthy AI. The NIST AI RMF is structured around four functions: Govern Establish policies, accountability, organisational roles, risk tolerances and oversight mechanisms for AI. Map Understand the purpose, context, stakeholders, potential impacts and operating environment of an AI system. Measure Assess, analyse and track AI risks using appropriate qualitative and quantitative methods. Manage Prioritise identified risks, implement controls, monitor responses and determine whether risks should be accepted, mitigated, transferred or avoided. AIGP Accuracy Note The four official functions are: Govern → Map → Measure → Manage “Monitor” is not a separate NIST AI RMF function. Monitoring activities may support the framework, but the fourth function is officially called Manage. Why it matters The NIST AI RMF helps organisations translate broad responsible-AI principles into practical governance activities. It can be adapted across industries and used alongside privacy, cybersecurity, enterprise-risk and compliance programmes. For AIGP candidates, the important point is to understand both the four functions and the iterative relationship between them. 2. European Union Artificial Intelligence Act The EU AI Act is not a voluntary framework. It is a legally binding regulation governing the development, deployment and use of AI systems within its scope. The Act entered into force on 1 August 2024 and follows a phased implementation timeline. Prohibited AI practices and AI-literacy requirements began applying in February 2025. Obligations concerning general-purpose AI models began applying in August 2025. Most remaining provisions are scheduled to become applicable from 2 August 2026, while certain requirements for high-risk AI systems connected with regulated products follow a later timeline. The Act applies a risk-based regulatory model. Prohibited AI practices Certain practices presenting unacceptable risks to fundamental rights are prohibited. These include specific forms of social scoring, manipulative AI, biometric categorisation and other practices defined by the regulation. The prohibitions are specific. It would be inaccurate to assume that every use of surveillance, biometrics or automated monitoring is automatically banned. High-risk AI systems AI used in sensitive areas such as employment, education, essential services, law enforcement and certain regulated products may be classified as high risk. Depending on the system and the organisation’s role, requirements may include: Transparency obligations Certain AI systems must disclose that users are interacting with AI. Additional transparency requirements may apply to synthetic content, deepfakes and general-purpose AI models. Minimal or no-risk systems Many ordinary AI applications remain largely unaffected, although organisations may still voluntarily adopt codes of conduct and responsible-AI practices. AIGP Accuracy Note The EU AI Act was not adopted in late 2023 and is no longer merely “expected to take effect.” It entered into force in August 2024, and several of its provisions are already applicable. Why it matters The EU AI Act moves AI governance from voluntary principles to enforceable responsibilities. Its influence is also likely to extend beyond Europe because organisations offering AI systems or services in the EU may fall within its scope. AIGP candidates should understand the difference between prohibited practices, high-risk requirements, transparency obligations and general-purpose AI responsibilities. 3. ISO/IEC 42001 and ISO/IEC 23894 ISO and the International Electrotechnical Commission have developed complementary standards for AI governance and risk management. Although they are frequently discussed together, ISO/IEC 42001 and ISO/IEC 23894 serve different purposes. ISO/IEC 42001:2023 ISO/IEC 42001 establishes requirements for an Artificial Intelligence Management System. It helps an organisation build an enterprise-wide system of policies, roles, objectives, processes and controls for the responsible development or use of AI. The standard follows the Plan-Do-Check-Act model commonly used across ISO management-system standards. It addresses areas such as: Because ISO/IEC 42001 is a requirements-based management-system standard, an organisation may pursue certification through an independent certification body. ISO/IEC 23894:2023 ISO/IEC 23894 provides guidance on managing risks specifically associated with AI. It helps organisations integrate AI-related risks into their existing risk-management activities and considers risks affecting organisations, individuals, groups and society. The standard can support AI risk identification, analysis, evaluation, treatment, communication and monitoring. AIGP Accuracy Note ISO/IEC 42001 is an AI management-system requirements standard against which an organisation may be certified. ISO/IEC 23894 is a risk-management guidance document. It is not a management-system certification standard. Why they matter Together, the two standards provide complementary value. ISO/IEC 42001 helps establish the organisational management system, while ISO/IEC 23894 provides deeper guidance for managing AI-specific risks within that system. For AIGP professionals, understanding this distinction is important when advising organisations about governance implementation and certification. 4. OECD Artificial Intelligence Principles The OECD AI Principles were originally adopted in 2019 and updated in May 2024 to address developments involving general-purpose and generative AI. They were the first intergovernmental standard for trustworthy AI and have influenced national policies, international initiatives and other governance instruments. The principles
You Don’t Need 10 Certifications to Get Into Cybersecurity—You Need These 5 Skills
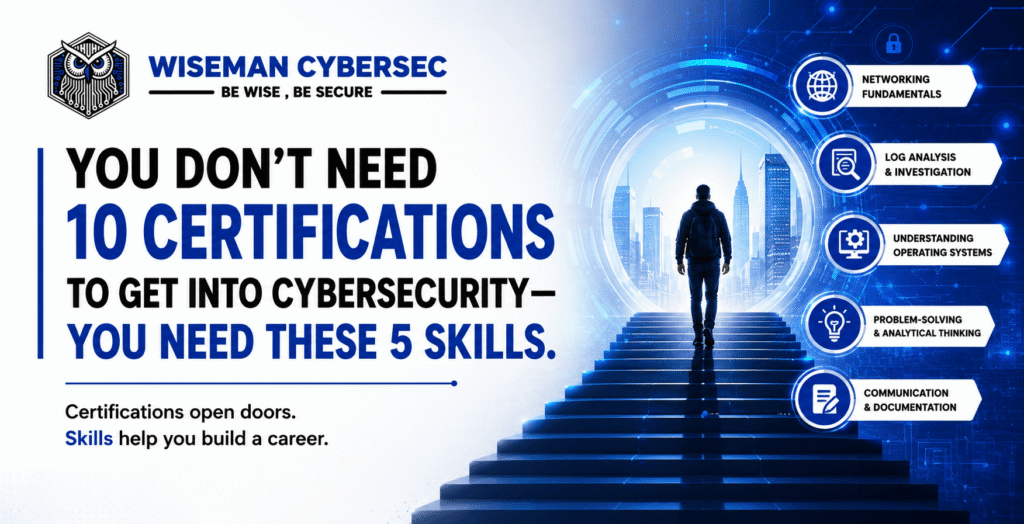
A cybersecurity beginner opens LinkedIn and sees the same advice everywhere. Get certified. Then get another certification. Then another one. Before long, the goal of building a cybersecurity career quietly turns into a race to collect certificates. CEH. Security+. CySA+. CISSP. CISM. ISO 27001. Maybe a few more just to make the resume look stronger. And yet, when the person finally sits in front of a recruiter or enters a real security environment, one simple question can expose the gap: “You have received an alert for multiple failed logins. How would you investigate it?”Suddenly, knowing the names of ten certifications does not help much. This is an uncomfortable truth about starting a cybersecurity career: Certifications can demonstrate that you studied something. They do not automatically prove that you can do the job. The cybersecurity industry does not need more people who can simply list security concepts. It needs people who can think, investigate, understand systems, and respond to problems. So, if you are trying to enter cybersecurity, stop asking yourself: “Which certification should I do next?”Start asking: “Which skills would make me useful in a real security team?” Here are five skills that matter far more than most beginners realise. 1. Networking Fundamentals: You Cannot Secure What You Do Not Understand Let’s start with the foundation. You do not need to become a network engineer to work in cybersecurity. But you absolutely need to understand how networks work. A surprising number of cybersecurity beginners try to learn advanced tools before understanding basic networking concepts. They know the name of a SIEM. They have seen an EDR dashboard. They can explain what a firewall does. But ask them to explain the difference between TCP and UDP, or what happens when a user visits a website, and the answer becomes uncertain. This creates a serious problem. Imagine an alert showing suspicious outbound traffic from an internal workstation. How do you determine whether it is malicious? You need to understand: Without this foundation, you are simply looking at an alert. You are not investigating it. Networking knowledge helps you understand the story behind the data. And cybersecurity is largely about understanding stories. What happened? Where did it start? What did it communicate with? What changed? A strong cybersecurity professional does not just say, “There is suspicious traffic.” They ask: “Why is this system communicating with that destination, over that port, at this time?” That is the beginning of real security thinking. 2. Log Analysis: Learn to Read What Systems Are Telling You Security teams generate an enormous amount of data. Login events. Firewall logs. Endpoint alerts. Authentication records. Cloud activity. Application events. The problem is not a lack of information. The problem is understanding what information actually matters. This is where log analysis becomes one of the most important skills in cybersecurity. Consider this: A user successfully logged in at 10:00 AM. On its own, this is completely normal. Now add a few more events: Suddenly, the individual events tell a very different story. The skill is not simply reading logs. The skill is connecting events. A good SOC analyst learns to identify patterns. They ask: This is why someone with strong analytical skills can sometimes outperform someone with more certifications. Because cybersecurity is not a multiple-choice exam. In the real world, the answer is often hidden across hundreds of events. You need to know how to find it. 3. Understanding Operating Systems: Know What Happens Behind the Interface Many cybersecurity learners focus heavily on tools. But tools are only as useful as your understanding of the systems they monitor. You should understand the basics of operating systems, particularly Windows and Linux. Why? Because attackers interact with operating systems. They create processes. They modify files. They use services. They create accounts. They execute commands. They manipulate permissions. If you do not understand normal system behaviour, malicious behaviour becomes much harder to recognise. For example, imagine an alert showing a suspicious PowerShell command. A beginner may simply see: “PowerShell detected.” An experienced analyst asks: The difference is knowledge. You do not need to memorise every command in Windows or Linux. But you need to understand how systems behave. You need to know what normal looks like. Because in cybersecurity, anomalies only make sense when you understand the baseline. 4. Problem-Solving: Cybersecurity Is Not a Checklist This may be the most underrated cybersecurity skill. Cybersecurity rarely gives you a perfectly labelled problem. You will not always receive an alert saying: “This is a phishing attack. Please follow steps 1 to 5.” Real incidents are messy. Information may be incomplete. The alert may be misleading. Multiple systems may be involved. And sometimes, the first assumption is completely wrong. This is why problem-solving matters. A strong cybersecurity professional is comfortable asking: “What else could explain this?” For example, a suspicious login could be: The job is not to immediately label everything as an attack. The job is to investigate. Good problem-solving means: This is also why cybersecurity professionals should not be afraid of saying: “I don’t know yet.” The important word is yet. The ability to investigate and find the answer is more valuable than pretending to know everything. 5. Communication and Documentation: The Skill Nobody Talks About Enough Cybersecurity is technical. But cybersecurity is also communication. You may investigate an incident perfectly. You may identify the root cause. You may even contain the threat. But if you cannot clearly explain what happened, your work loses value. A security analyst may need to communicate with: And each audience needs a different level of explanation. A CISO may not need to know every command executed on a system. But they need to know: What happened? What was affected? What is the business impact? What is being done about it? This is where clear documentation matters. A good incident report should help someone understand the incident even if they were not part of the investigation. Poor documentation creates confusion. It also makes future investigations harder. In cybersecurity, your
The Kudankulam Data Breach: What India’s Critical Infrastructure Can Teach Us About Third-Party Risk
The most dangerous assumption in cybersecurity is that your security ends at your firewall. On 15 July 2026, a report about India’s Kudankulam Nuclear Power Plant created a wave of concern across the cybersecurity and critical infrastructure community. A ransomware group reportedly published a large cache of files on the dark web that were allegedly linked to Reliance Group and related to infrastructure work at Kudankulam’s Units 3 and 4. According to reporting, the data was associated with a server hosted by Yotta, a third-party data centre provider. Reliance acknowledged a partial breach of its data and said the government had been informed. The reported files included purported blueprints, supplier details, inspection records and other project-related documents. The authenticity of the documents and the full extent of the exposure remain under investigation. Let us be precise about something. This is not a story about an attacker remotely taking control of a nuclear reactor. And that distinction matters. The Indian government had previously stated, in relation to the 2019 KKNPP malware incident, that the infection was limited to the administrative network and that the plant’s control and instrumentation systems were isolated from external and administrative networks. But here is the uncomfortable lesson: An organisation does not need to lose control of its most critical system for a cyber incident to become strategically dangerous. Sometimes, the breach happens somewhere else. With someone else. On infrastructure you do not directly operate. And yet the information exposed may still be connected to your most sensitive assets. That is the real third-party risk lesson emerging from the Kudankulam case. The breach did not have to start inside the nuclear plant When people hear “critical infrastructure cybersecurity,” they usually imagine the obvious attack scenario. An attacker finds a vulnerability in a plant network. They bypass a firewall. They gain access to an OT environment. They compromise an industrial control system. The story is easy to understand because the attack follows the traditional perimeter model. But modern attacks do not always work that way. The Kudankulam case, as currently reported, presents a different and much more uncomfortable model. The reported chain looks something like this: Critical infrastructure project → contractor → third-party data centre → stored project data → ransomware attack → public exposure The attacker may not need to breach the nuclear facility directly. They may not need access to a reactor control system. They may not even need to understand the entire plant architecture. They may only need to find a connected organisation holding sensitive information related to the project. This is the fundamental shift in third-party risk. Your attack surface is no longer defined by the systems you own. It is defined by the systems that hold your data, connect to your operations, support your projects, or are trusted by your people. The data may be “administrative”. The intelligence may not be. One of the most dangerous words in cybersecurity is administrative. An administrative system is often mentally categorised as less important than an operational system. That is understandable. An office network is not a reactor control system. A project document is not a PLC. A supplier database is not a safety system. But attackers do not always look at data through the same lens as defenders. A document that looks “administrative” to an organisation may provide an adversary with context. Supplier information can reveal dependencies. Inspection records can reveal equipment and maintenance patterns. Project documents can reveal how different organisations interact. Engineering documentation can reveal design assumptions or infrastructure relationships. Insurance documents can expose how an organisation categorises and financially models certain risks. Individually, each document may appear harmless. The problem is aggregation. A threat actor does not necessarily need one magical document. They may need thousands of small pieces of information that, when combined, create a much clearer picture of the target. This is why data classification cannot be based only on the question: “Can this file directly control a critical system?” The better question is:“What could an adversary understand if they collected enough of our data?” The vendor is not “just a vendor” anymore For years, many organisations have treated third-party risk as a procurement activity. A vendor is selected. A questionnaire is sent. A certificate is requested. A contract is signed. The vendor is onboarded. And the security team moves on to the next problem. This approach is increasingly inadequate. NIST describes cybersecurity supply chain risk management as the process of identifying, assessing and mitigating risks across the interconnected ICT and OT supply chain throughout the lifecycle of systems and services. That lifecycle includes design, development, deployment, maintenance and even destruction. That is a very different way of thinking about vendors. A vendor is not simply a company that provides a service. A vendor is a security dependency. And every security dependency creates a question: What happens to our risk when our data, access or operations move into their environment? In the Kudankulam case, the reported involvement of a third-party data centre provider is precisely what makes the story relevant to almost every modern organisation. Because most companies today rely on someone else. Cloud providers. Managed service providers. Data centres. SaaS platforms. Payroll systems. IT support vendors. Consultants. Engineering contractors. Software suppliers. And increasingly, AI platforms. The perimeter is no longer a wall. It is an ecosystem. The “weakest link” analogy is no longer enough Cybersecurity professionals often say: “Your security is only as strong as your weakest link.” It sounds correct. But it is incomplete. The problem is that third-party risk is not always about finding the weakest vendor. It is about understanding where trust has been transferred. A highly mature organisation may have excellent internal controls. Strong MFA. A capable SOC. Endpoint detection. Segmentation. Incident response. But if a critical supplier has access to sensitive project data and operates with weaker controls, the risk does not disappear simply because the primary organisation is mature. In fact, attackers may deliberately target the supplier. NIST has explicitly highlighted that
How Third-Party Vendor Breaches Become Enterprise Security Crises
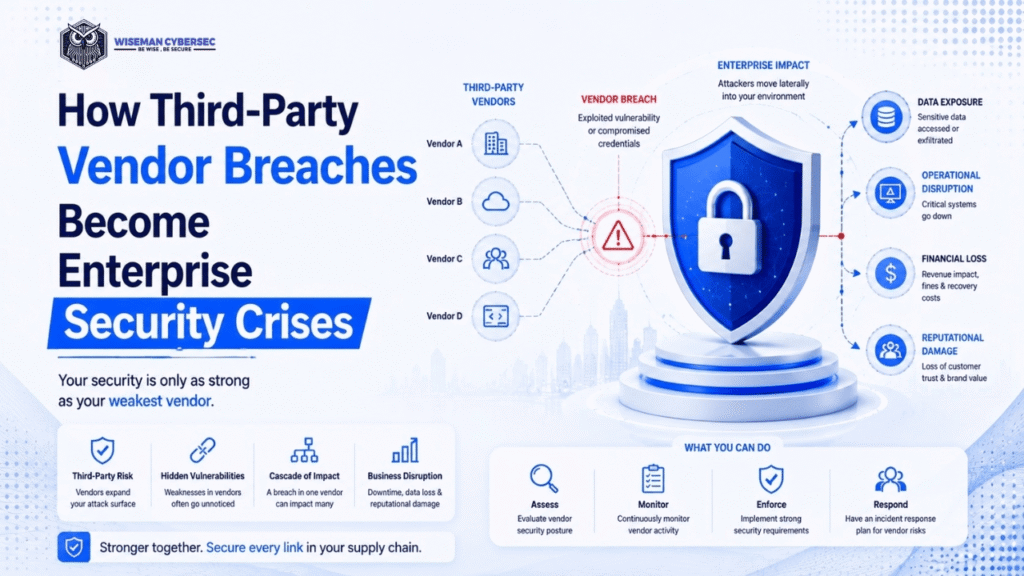
Introduction: In today’s interconnected digital ecosystem, cybersecurity extends far beyond an organization’s own network. Businesses increasingly rely on cloud platforms, SaaS applications, managed service providers (MSPs), consultants, payroll vendors, IT outsourcing firms, and numerous third-party partners to support critical operations. While these partnerships drive innovation and efficiency, they also introduce significant security risks. Every external vendor with access to your systems, applications, or sensitive data becomes part of your organization’s extended attack surface. If that vendor is compromised, the consequences can quickly escalate into a full-scale enterprise security crisis. Recent supply chain attacks have demonstrated that cybercriminals often target trusted third parties instead of attacking organizations directly. A single vulnerable supplier can become the gateway to data breaches, ransomware attacks, operational disruptions, regulatory penalties, and lasting reputational damage.Understanding and managing third-party risk is no longer optional—it’s a fundamental component of modern cybersecurity. Understanding Third-Party Risk: Third-party risk refers to the potential cybersecurity, operational, financial, and compliance risks introduced by external organizations that have access to your business assets. These vendors may include: Many organizations invest heavily in securing their own infrastructure while overlooking the security posture of their vendors. Unfortunately, attackers understand this weakness. A small supplier with privileged access can often become the easiest route into a much larger enterprise. This is why Third-Party Risk Management (TPRM) has evolved from a procurement requirement into a strategic cybersecurity function. How Vendor Breaches Become Enterprise Security Crises: A third-party breach becomes an enterprise-wide incident when attackers leverage the trust established between a vendor and the organization. Common attack vectors include: Once attackers gain access through a trusted vendor, they frequently: Because the traffic originates from trusted partners, malicious activity often goes undetected for extended periods, increasing the overall impact of the attack. Common Attack Paths: Third-party compromises generally follow predictable patterns. 1. Credential Theft: Attackers steal vendor usernames and passwords through phishing, malware, or credential leaks and use them to access customer environments. 2. Software Supply Chain Attacks: Cybercriminals compromise a vendor’s software development or update process, allowing malicious code to be distributed to thousands of customers simultaneously. 3. Remote Access Exploitation: Many IT vendors require administrative access to customer systems. Poorly secured remote access tools can become attractive entry points for attackers. 4. API Abuse: Insecure APIs between vendors and organizations may expose sensitive information or provide unauthorized system access. 5. Shared Infrastructure: Organizations that rely on shared cloud environments or integrated platforms may experience cascading compromise when a provider is breached. Business Impact of Third-Party Breaches: The consequences extend far beyond technical recovery. Data Exposure: Sensitive customer information, financial records, intellectual property, and confidential business data may be compromised. This often triggers: Operational Disruption: Critical business operations can come to a halt when vendors providing essential services become unavailable. Examples include: Financial Losses: Organizations frequently incur significant expenses, including: Reputational Damage: Customers rarely distinguish whether a breach originated internally or through a vendor. Loss of trust can result in: Why Traditional Vendor Assessments Fall Short: Many organizations still rely on annual questionnaires and compliance checklists to assess vendor security. While useful, these methods provide only a snapshot in time. Cyber threats evolve daily. A vendor that appeared secure during onboarding may experience a breach weeks later. Traditional assessments often fail because they: Effective Third-Party Risk Management requires ongoing visibility—not just periodic reviews. What Strong Vendor Security Looks Like: A mature vendor security program begins before a contract is signed. Organizations should: Security expectations should also be embedded into contracts, including: Vendor security should remain a continuous process throughout the business relationship. Practical Controls That Reduce Third-Party Risk: Organizations can significantly reduce exposure by implementing layered security controls. Recommended best practices include: Organizations should also maintain a complete inventory of vendors and identify which ones have access to critical systems or sensitive information. Evidence-based validation—such as independent security audits, penetration testing reports, and vulnerability management practices—is far more reliable than relying solely on vendor questionnaires. Governance Is the Key to Success: Third-party risk cannot be managed by cybersecurity teams alone. An effective TPRM program requires collaboration across multiple departments. Security Teams: Procurement: Legal Teams: Business Owners: Shared ownership reduces blind spots and enables faster decision-making during security incidents. Building a Mature Third-Party Risk Management Program: A comprehensive TPRM framework typically includes: Modern organizations increasingly use automation and continuous monitoring platforms to prioritize high-risk vendors and reduce assessment fatigue. The objective is not to eliminate every risk but to identify, prioritize, and effectively manage the risks that matter most. Final Thoughts: Third-party vendor breaches have become one of the most significant cybersecurity threats facing modern organizations. Attackers understand that trusted relationships often provide easier access than attacking well-defended enterprises directly. Without continuous oversight, strong governance, and enforceable security controls, a single vendor compromise can rapidly evolve into an enterprise-wide security crisis. Organizations that proactively invest in Third-Party Risk Management are better positioned to protect sensitive data, maintain business continuity, satisfy regulatory requirements, and preserve customer trust. In an era of increasingly interconnected digital ecosystems, cybersecurity is only as strong as the weakest link in your supply chain. Strengthening vendor security today is essential to protecting your organization tomorrow. – Wiseman CyberSec Secure Your Vendor Ecosystem Before Attackers Do– Third-party vendors shouldn’t become your biggest cybersecurity risk. Strengthen your supply chain security with expert-led Third-Party Risk Management, Vendor Risk Assessments, and Cybersecurity Training from Wiseman CyberSec.
SOC Analyst vs DFIR Analyst vs Threat Hunter: Understanding the Real Difference
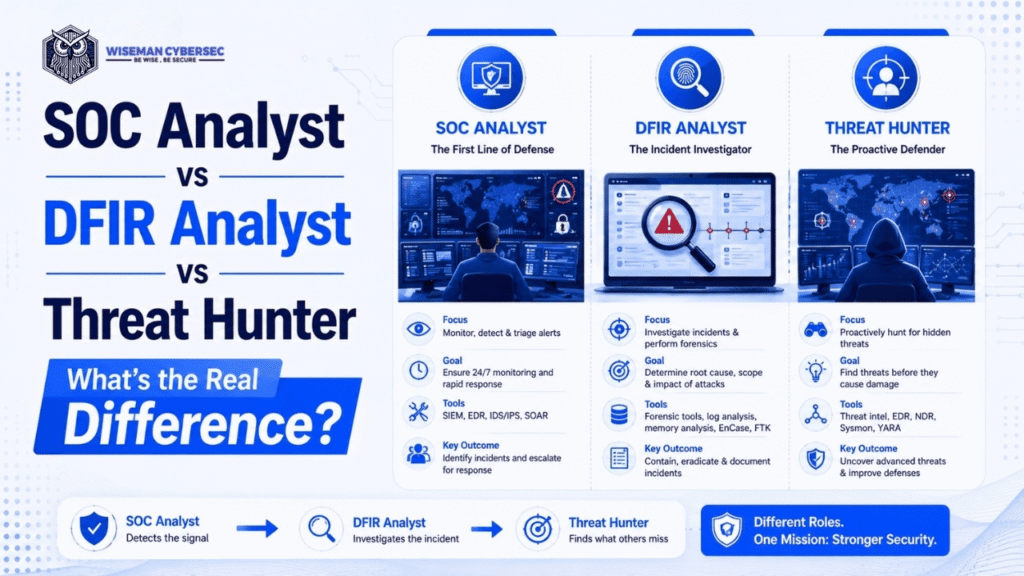
Introduction: As cyber threats become more sophisticated, organizations need specialized cybersecurity professionals to protect their environments at every stage of an attack. While the terms SOC Analyst, DFIR Analyst, and Threat Hunter are often used together, each role serves a distinct purpose within a mature Security Operations Center (SOC).Think of cybersecurity as a continuous defense cycle. One professional monitors for suspicious activity, another investigates and responds to confirmed incidents, while a third proactively searches for threats that traditional security tools may have missed.Although these roles work closely together, understanding their responsibilities, skill sets, and objectives is essential for organizations building security teams and for professionals planning a career in cybersecurity. The Cybersecurity Defense Lifecycle: A successful Security Operations Center follows a layered approach to cyber defense: Together, they create a comprehensive security strategy that helps organizations detect, respond to, and prevent cyberattacks. SOC Analyst – The First Line of Defense: A Security Operations Center (SOC) Analyst is responsible for continuously monitoring an organization’s network, systems, endpoints, and security tools for signs of malicious activity.Their primary objective is to identify, validate, and triage security alerts before they escalate into major incidents. Primary Responsibilities: Common Tools: SOC Analysts typically work with: Key Skills: Goal: Identify threats as quickly as possible and ensure rapid escalation to minimize business impact. DFIR Analyst – The Incident Investigator: Digital Forensics and Incident Response (DFIR) Analysts take over once a security incident has been confirmed. Rather than focusing on detection, they investigate exactly how the attack occurred, what systems were affected, how attackers gained access, and what evidence can be preserved. Their work combines technical investigation with structured incident response. Primary Responsibilities: Common Tools: DFIR professionals commonly use: Key Skills: Goal: Contain the incident, eradicate the threat, recover affected systems, and prevent similar attacks in the future. Threat Hunter – The Proactive Defender: Unlike SOC Analysts who respond to alerts, Threat Hunters actively search for threats that have not yet triggered security controls. Threat Hunting is hypothesis-driven and intelligence-led. Instead of waiting for alerts, Threat Hunters assume attackers may already be inside the environment and proactively look for indicators of compromise. This role requires strong analytical thinking and deep knowledge of attacker techniques. Primary Responsibilities: Common Tools: Threat Hunters frequently use: Key Skills: Goal: Discover threats before they become active security incidents and continuously strengthen the organization’s defensive posture. Comparing the Three Roles: SOC Analyst DFIR Analyst Threat Hunter How These Roles Work Together: These roles are not competitors—they complement each other as part of a unified cybersecurity defense strategy. A typical workflow looks like this: This collaborative approach enables organizations to respond faster, reduce attacker dwell time, and continuously strengthen their overall security posture. Which Career Path Should You Choose? Choosing between these roles depends on your interests and career goals. Choose SOC Analyst if you enjoy: Choose DFIR Analyst if you enjoy: Choose Threat Hunter if you enjoy: Many cybersecurity professionals begin as SOC Analysts before progressing into DFIR, Threat Hunting, Detection Engineering, or Security Architecture roles. Final Thoughts: Cybersecurity is no longer about a single role protecting an organization. Modern defense requires a coordinated team where each specialist contributes at a different stage of the attack lifecycle. SOC Analysts detect the signals, DFIR Analysts investigate and contain incidents, and Threat Hunters proactively uncover threats that traditional security controls may miss. Together, these professionals help organizations reduce risk, respond effectively to incidents, and build resilient security operations. Whether you’re starting your cybersecurity journey or expanding your Security Operations Center, understanding these distinct roles is essential for building a stronger, more proactive cyber defense strategy. – Wiseman CyberSec Advance Your Career in Cybersecurity Master the skills required for roles like SOC Analyst, DFIR Analyst, Threat Hunter, Security Analyst, and Incident Responder with Wiseman CyberSec’s hands-on cybersecurity training programs. Explore Our Cybersecurity & AI Security Courses and take the next step toward a successful career in cyber defense.
5 Common ISO 27001 Audit Mistakes Organizations Still Make
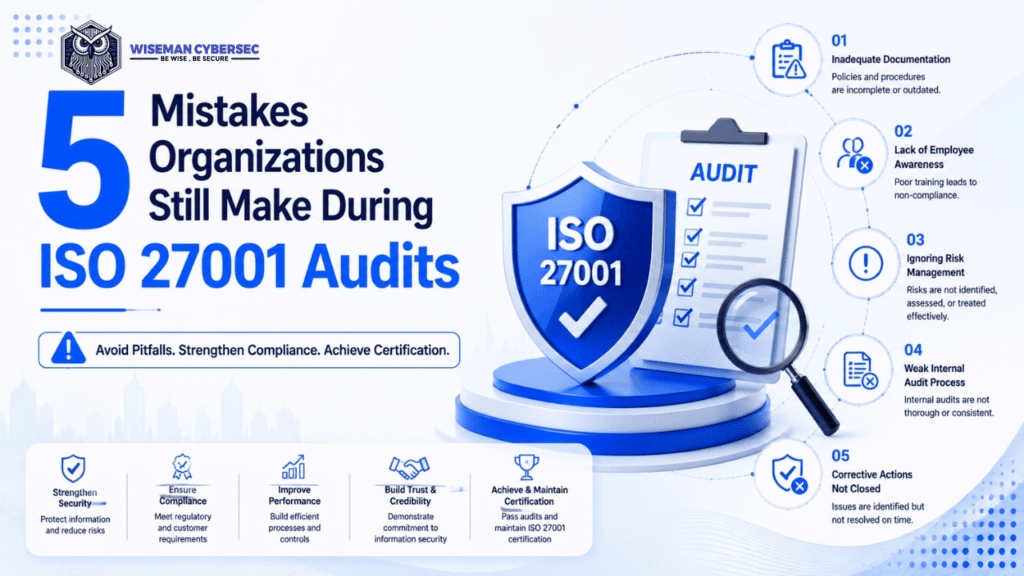
ISO 27001 certification is one of the most effective ways to demonstrate a strong information security management system. It helps organizations protect sensitive data, build customer trust, and show that security is managed through a structured and repeatable process. However, many organizations still struggle during audits because of avoidable mistakes that weaken compliance and create unnecessary findings. The good news is that most ISO 27001 audit issues are preventable. With the right documentation, employee awareness, risk management, internal audit discipline, and corrective action process, organizations can significantly improve their audit readiness and certification success. Why ISO 27001 audits matter: An ISO 27001 audit is not just a formal review of documents. It evaluates whether your organization’s information security management system is working in practice, not just on paper. Auditors want to see evidence that policies are implemented, risks are managed, employees are aware of their responsibilities, and corrective actions are tracked properly. For leadership, a successful audit reflects maturity, accountability, and resilience. For teams, it creates clarity around responsibilities and helps build a culture of security. That is why audit preparation should be treated as an ongoing business activity rather than a last-minute project. 1. Inadequate documentation: One of the most common reasons organizations struggle during an ISO 27001 audit is poor documentation. Policies may be incomplete, outdated, or not aligned with actual business processes. In some cases, documents exist only to satisfy the standard, but they are not actively used or reviewed. Auditors look for consistency between written policies and real-world practices. If the documentation says one thing and the organization does another, that inconsistency can lead to nonconformities. Strong documentation should be current, approved, version-controlled, and easy for relevant staff to access. How to avoid it: 2. Lack of employee awareness: Even the best policies fail if employees do not understand them. A common audit issue is weak security awareness across the workforce, especially when people cannot explain basic responsibilities such as incident reporting, password hygiene, access control, or data handling practices. ISO 27001 expects organizations to show that security awareness is part of daily operations. Training records alone are not enough if employees cannot apply what they learned. Auditors often ask staff how they would respond to phishing emails, suspicious activity, or unauthorized access attempts. How to avoid it: 3. Ignoring risk management: Risk management is the foundation of ISO 27001, yet many organizations treat it like a one-time compliance exercise. They complete a risk assessment during implementation but fail to update it when systems, vendors, regulations, or business processes change. This creates a disconnect between the ISMS and the actual risk environment. Auditors expect risk assessment and treatment to be active, not static. Risks should be identified, evaluated, assigned, treated, and reviewed on a regular basis. If the risk register is outdated, it suggests that the organization is not managing information security in a structured way. How to avoid it: 4. Weak internal audit process: Many organizations treat internal audits as a formality before the certification audit. That approach is risky because internal audits are meant to identify weaknesses early and help the organization improve before external auditors arrive. A weak internal audit process often means gaps are discovered too late or not at all. A good internal audit should be independent, risk-based, and thorough. It should cover applicable clauses, controls, and operational evidence. If internal audits are rushed or performed without proper expertise, the organization loses one of its most valuable tools for maintaining audit readiness. How to avoid it: 5. Corrective actions not closed: Another major audit mistake is failing to close corrective actions properly. Organizations may identify a nonconformity but then delay root cause analysis, correction, or follow-up. This creates repeat issues and weakens confidence in the management system. ISO 27001 auditors expect a complete corrective action cycle: identify the issue, determine the root cause, implement a fix, verify effectiveness, and document closure. If this process is inconsistent, the organization may appear reactive rather than mature and controlled. How to avoid it: What auditors look for : Auditors are not only checking whether you have documents in place. They are looking for evidence of discipline, consistency, and continuous improvement. They want to see that leadership is involved, employees understand their roles, risks are actively managed, and corrective actions are tracked effectively. A well-prepared organization usually demonstrates: How to improve audit readiness: The best way to prepare for an ISO 27001 audit is to make readiness part of everyday operations. Organizations that wait until the audit date is near often struggle with missing evidence, untrained staff, and unresolved actions. In contrast, organizations that build regular reviews into their ISMS are far more likely to succeed. A practical preparation cycle includes reviewing documentation, checking risk assessments, testing staff awareness, running internal audits, and closing any open findings. This creates a stronger system and reduces stress when the external audit begins. Final thoughts: ISO 27001 audits do not have to be stressful. Most problems come from preventable weaknesses rather than complex technical failures. By improving documentation, awareness, risk management, internal audits, and corrective action closure, organizations can build a more reliable and audit-ready ISMS. If your goal is certification, focus on consistency over speed and evidence over assumptions. A well-managed ISMS not only helps you pass the audit but also strengthens your long-term security posture. – Wiseman CyberSec Ready to simplify your ISO 27001 audit journey? Avoid common audit pitfalls with expert guidance from WisemanCyberSec. Whether you’re preparing for certification, conducting internal audits, or strengthening your ISMS, our cybersecurity professionals can help you achieve compliance with confidence. Contact WisemanCyberSec today to schedule an ISO 27001 consultation and assess your audit readiness.
Why Cybersecurity Is No Longer Just Technical: A Business Imperative for Every Organization
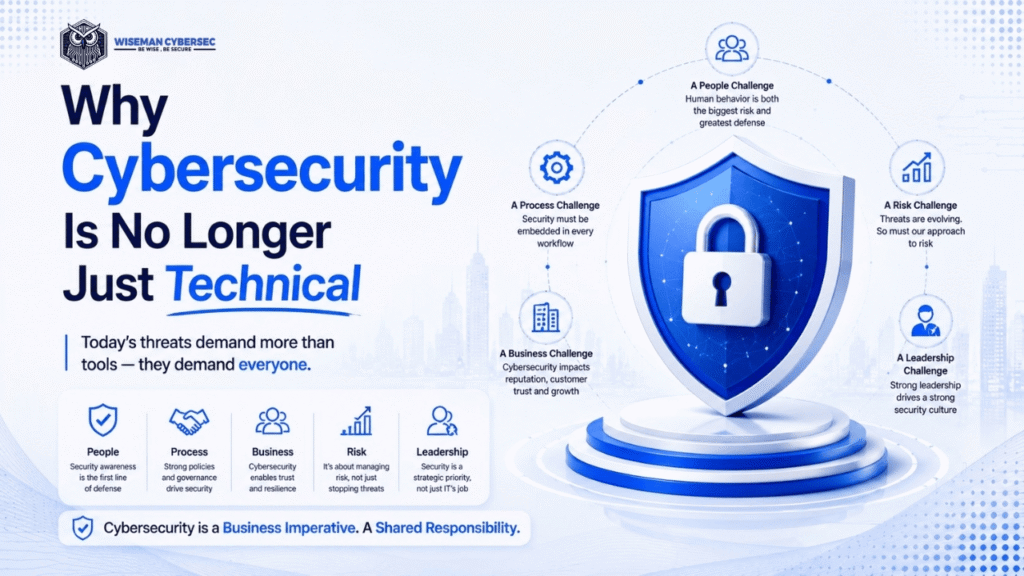
For many years, cybersecurity was treated as a narrow technical discipline owned by the IT department. Firewalls, antivirus tools, patching, and network defenses were seen as the primary answer to security threats. That approach is no longer enough. Today’s threat landscape is more complex, more human-driven, and more business-critical than ever before. Cybersecurity now affects reputation, customer trust, compliance, operations, revenue, and long-term resilience. The central message of this post is clear: cybersecurity must be embedded across the entire organization. It is not just about protecting systems; it is about protecting the business itself. When security is viewed only as a technical issue, organizations tend to react late, overlook human behavior, and create gaps between policy and practice. A modern security program must connect technology with governance, culture, leadership, and business strategy. The shift from technical to strategic: Cyber threats have evolved far beyond basic malware or unauthorized access attempts. Attackers now exploit people through phishing, social engineering, credential theft, business email compromise, and insider misuse. They target business processes, third-party relationships, cloud environments, and supply chains. This means that defending an organization requires more than technical controls alone. Security leaders must now think strategically. Cybersecurity decisions affect hiring, training, procurement, vendor selection, remote work policies, customer experience, and crisis management. In other words, security is not a separate layer added at the end; it is part of how the business operates from the beginning. The people challenge: Human behavior remains one of the biggest security risks. Employees can accidentally click malicious links, reuse weak passwords, mishandle sensitive data, or bypass procedures under pressure. At the same time, people are also the organization’s first and strongest line of defense when they are trained, informed, and empowered. This is why awareness programs alone are not enough. Organizations need a security culture where employees understand why controls exist and how their actions affect the company. That includes role-based training, leadership messaging, clear reporting channels, and practical guidance for everyday decisions. When people become part of the defense strategy, the organization becomes significantly harder to attack. The process challenge: Even the best security tools fail when processes are weak or ignored. Security must be embedded into workflows, not layered on as an afterthought. That means secure onboarding and offboarding, access reviews, change management, incident response procedures, backup testing, vendor risk checks, and documented approval paths. Strong processes create consistency. They reduce reliance on individual memory and ensure that security decisions are repeatable and measurable. In frameworks such as ISO 27001, this process-driven approach is essential because it ties security to governance, accountability, and continuous improvement. The goal is not just to prevent incidents, but to build an organization that can respond, recover, and adapt. The business challenge: Cybersecurity has direct business impact. A security incident can disrupt operations, delay services, damage client confidence, trigger legal exposure, and affect revenue. For customer-facing organizations, one breach can quickly become a reputation crisis. For regulated industries, the consequences may include fines, audits, and contractual loss. This is why business leaders must treat cybersecurity as a core business function. It is not merely a cost center or a technical overhead. It protects trust, preserves continuity, and supports growth. If the business depends on digital systems, customer data, and connected operations, then security is inseparable from business performance. The risk challenge: Risk is not static. Threats evolve, attackers adapt, and business environments change constantly. Remote work, cloud adoption, AI-enabled attacks, third-party dependencies, and shadow IT have expanded the attack surface. Security programs must therefore shift from a one-time control mindset to an ongoing risk management approach. A risk-based security strategy helps organizations prioritize what matters most. Not every asset carries the same level of exposure, and not every threat has the same business impact. Mature organizations assess likelihood and impact, apply controls where they matter most, and continuously review priorities as conditions change. This is what makes cybersecurity sustainable instead of reactive. The leadership challenge: Leadership determines whether cybersecurity becomes a real organizational priority or remains a technical checkbox. Strong leaders set the tone, allocate resources, demand accountability, and create a culture where security is taken seriously. Without leadership support, security teams often struggle to get buy-in for policy enforcement, training, investments, and process changes. Leaders do not need to be technical experts to support cybersecurity effectively. They do need to ask the right questions, understand business risk, and treat security as part of corporate governance. When executives visibly support security, teams across the organization are more likely to follow. That top-down commitment is often what separates mature organizations from vulnerable ones. Why shared responsibility matters: The post correctly frames cybersecurity as a shared responsibility. IT teams, security professionals, executives, managers, employees, vendors, and even customers all play a role in protecting the organization. No single team can stop every threat alone. Shared responsibility means that everyone has a part to play. Employees must follow secure practices, managers must enforce policies, executives must sponsor the program, and security teams must design practical controls that support business goals. When responsibility is distributed clearly, security becomes more resilient and far more effective. Building a modern security culture: A strong cybersecurity culture does not happen by chance. It is built through consistent communication, leadership commitment, process discipline, and ongoing education. Organizations should make security visible, understandable, and relevant to daily work. Practical steps include: These practices help move security from theory into daily behavior. Over time, they create an environment where secure choices become normal choices. Conclusion: Cybersecurity is no longer just a technical function because modern threats do not stay within technical boundaries. They affect people, processes, business operations, leadership decisions, and organizational risk. The most resilient organizations are the ones that treat security as a business imperative and a shared responsibility. – Wiseman CyberSec Ready to build a cybersecurity culture that protects your business? Explore Wiseman CyberSec’s cybersecurity, risk management, and governance training programs to empower your teams, strengthen resilience, and stay ahead of evolving threats.